OT Security

Full OT visibility starts now

Gain fast visibility into communicating assets, dependencies, and blind spots using telemetry you already have – without agents, active scanning, or disruption to production.

Start with what your network already knows

Icons - Video 3 (4)

Traditional OT security programs can spend months on planning, procurement, and sensor deployment before producing useful visibility. Exeon uses metadata from existing network and security infrastructure to establish an initial operational picture quickly and without changing production systems.

See what is there first. Then validate segmentation, strengthen compliance evidence, and target further investments where they matter most.

Connect existing telemetry

Flows, firewalls, switches, logs, DPI, and OT security tools.

Reveal the actual environment

Assets, dependencies, communication paths, and shadow OT.

Prioritize what comes next

Segmentation changes, targeted inspection, investigations, and compliance evidence

Our customers benefit from full visibility

Industry challenges

Your checklist: Overcome OT security challenges

What is actually communicating?

Which assets, legacy devices, remote connections, and dependencies exist across sites and zones?

Is segmentation working as intended?

Does observed traffic match documented architecture, firewall policy, and approved communication paths?

Can you prove controls are operating continuously?

Can you provide current evidence for NIS2, KRITIS, and IEC 62443, not just a point-in-time audit snapshot?

Can OT and the SOC investigate from the same evidence?

Can analysts understand an event without asking OT engineers to reconstruct the context manually?

Key statistics

Why OT security can’t wait

of all EU cybersecurity incidents now involve OT systems.

0 %

of recorded EU incidents hit NIS2-classified essential entities.

0 %

increase in newly disclosed vulnerabilities, often exploited within days.

0 %
Solution

How Exeon helps OT infrastructure

Keep what you have

Uses existing telemetry and protects current investments.

Broad, scalable behavioral visibility

Adds visibility across distributed and partially monitored environments.

Vendor-independent analytics

Correlates signals from multiple vendors.

Deploys flexibly

Supports cloud, self-hosted, and on-premises deployment.

100% confidentiality

Keeps data sovereignty and operational constraints in view.

Controlled scaling

Scales in phases rather than requiring a big-bang rollout.

Uncover your shadow OT

See what your OT network is not telling you

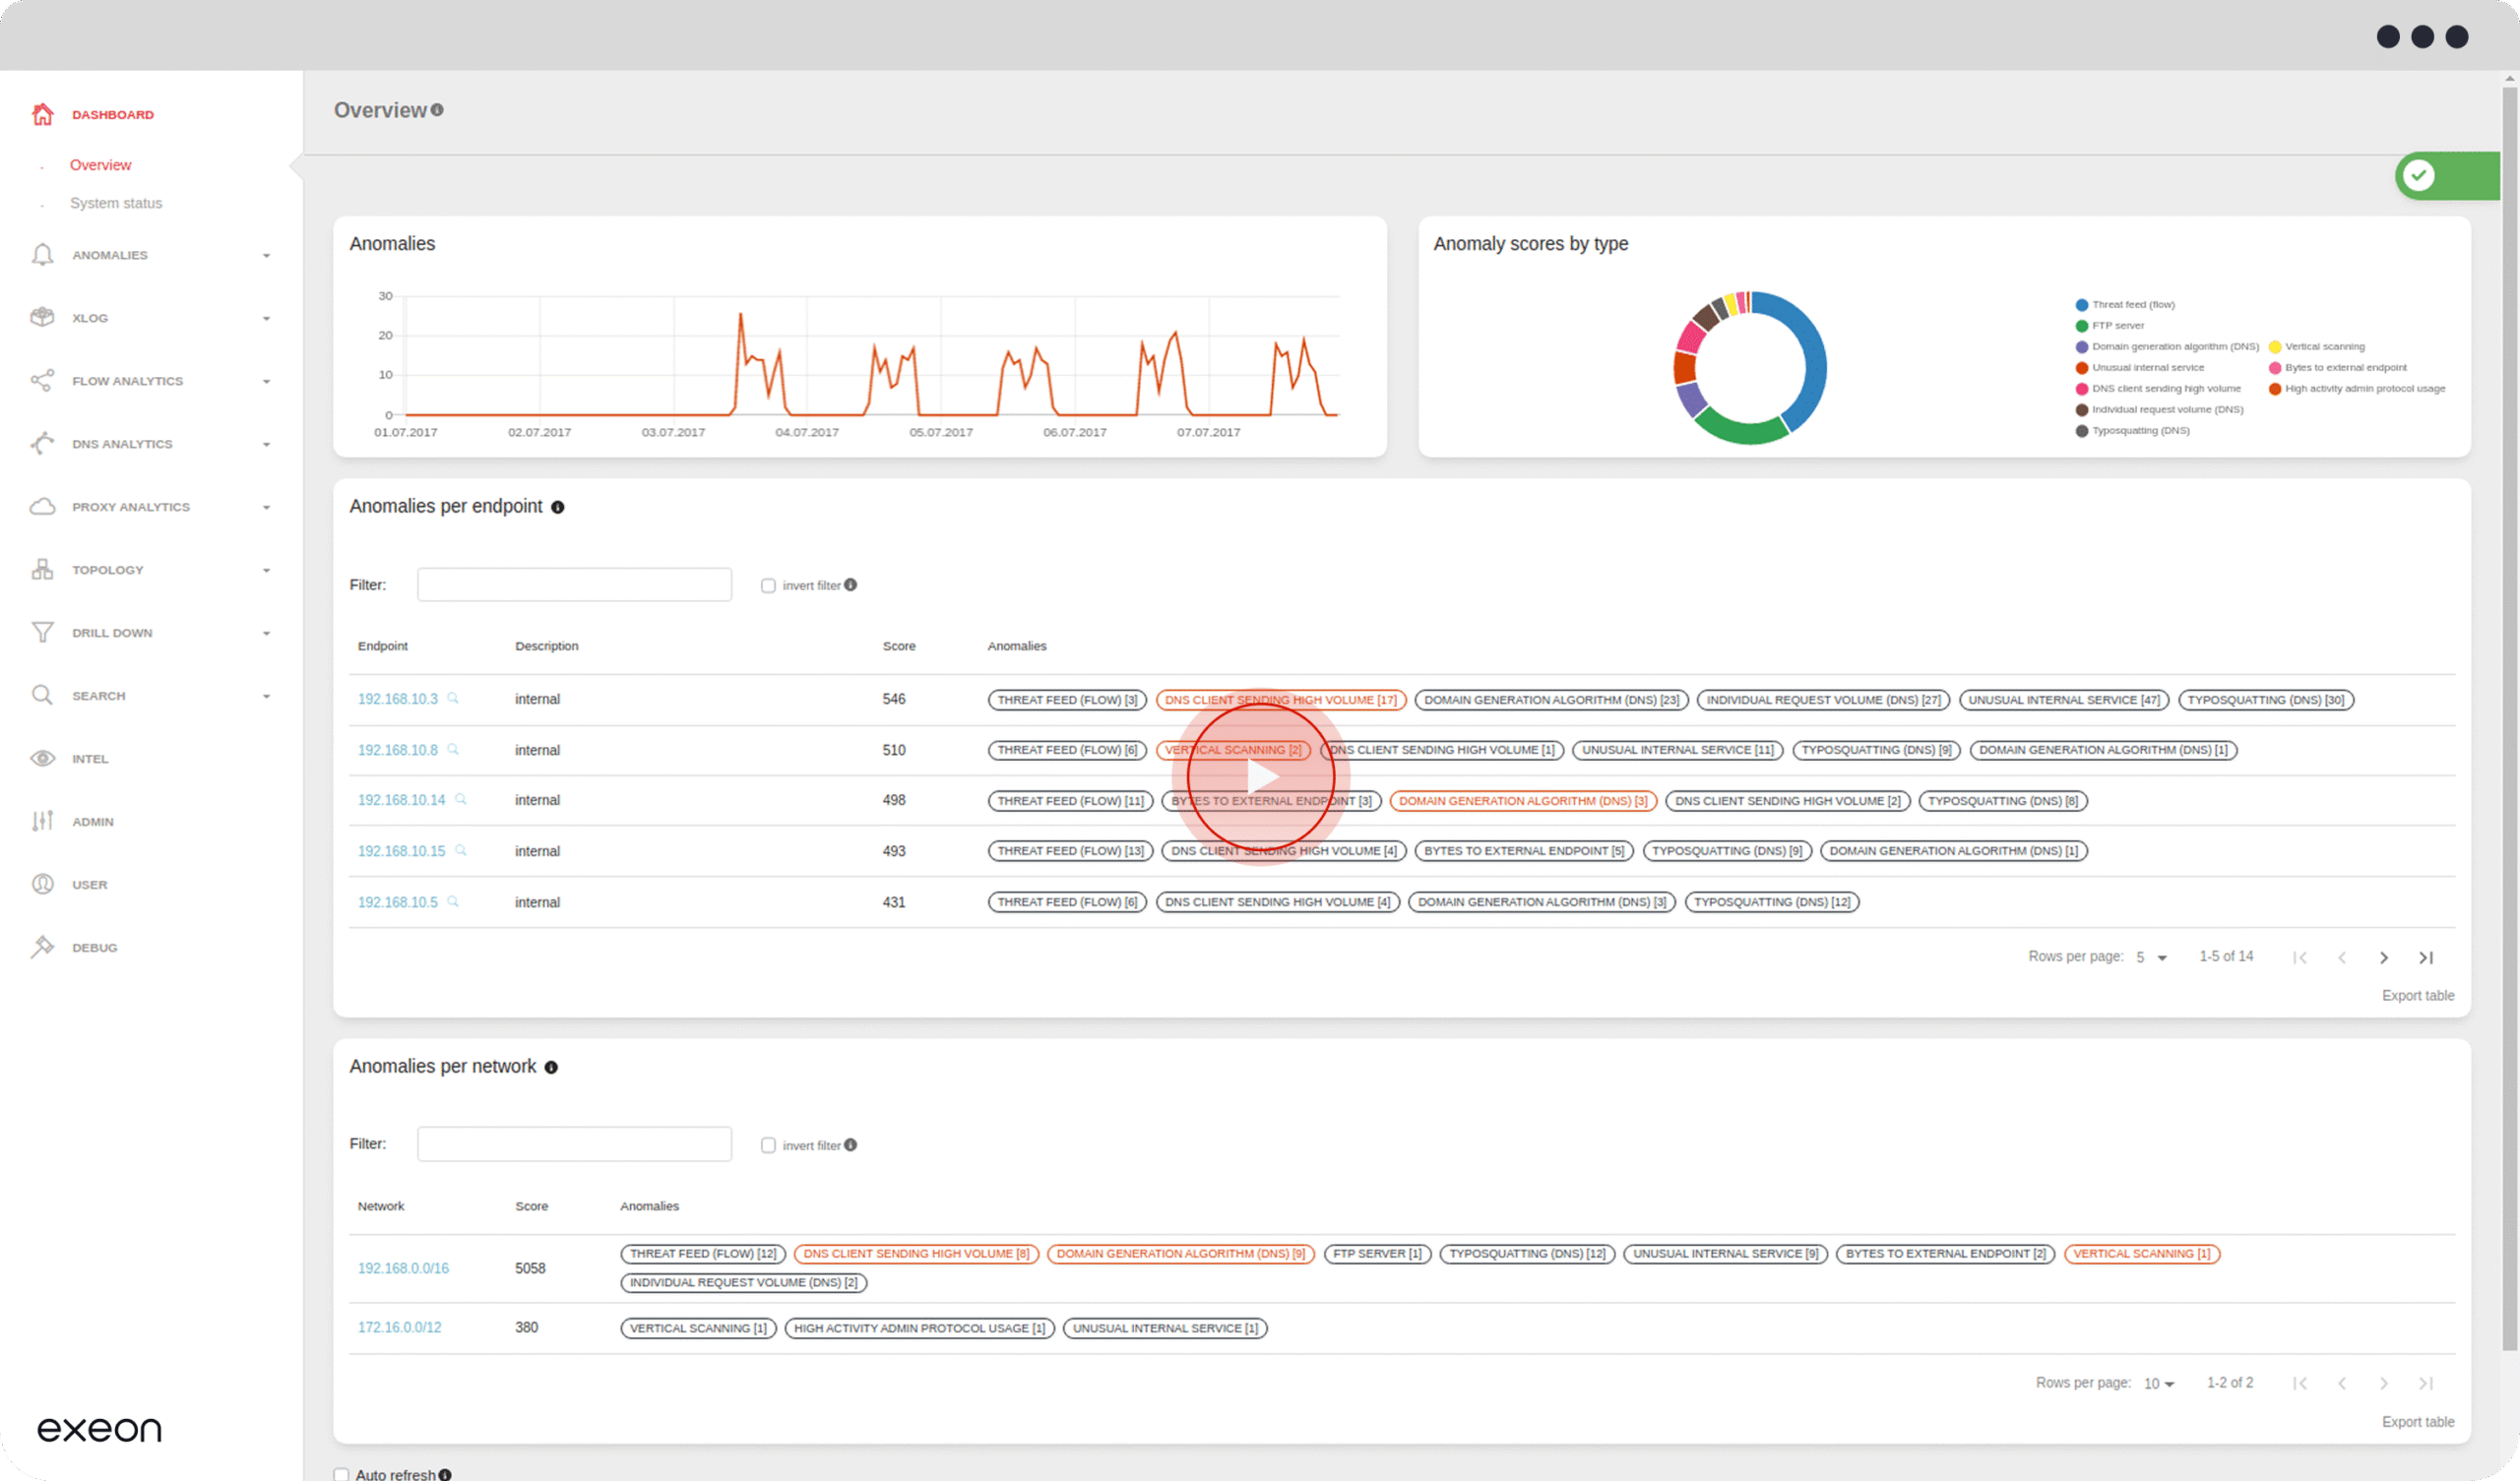
Unmanaged assets, undocumented connections, legacy systems, and forgotten remote-access paths can remain invisible to inventories and network diagrams. See how Exeon uses passive metadata analytics to expose what is actually communicating—without interrupting production.

Covering all stages of OT security

Purpose-built for OT security

OT security for full visibility with Exeon.
Whitepaper

Understand the approach

Why visibility should come before major OT investment.

Evaluation guide

Assess the current architecture

Evaluate visibility gaps, segmentation, and operational overhead.

Use case eBook

Explore practical scenarios

Exeon.NDR applied: Shadow OT, remote access, segmentation, and lateral movement.

Solution brief

Quick review of the solution

Understand the architecture, deployment model, and key capabilities.

Prepare for regulatory requirements

Compliance for OT

Translate NIS2, KRITIS & IEC 62443 into practical OT controls.

Why our customers choose visibility first

By integrating Exeon products, our valued customers gain unmatched network visibility, AI-driven detection and behavior analytics.

Additional solutions powered by Exeon products
Exeon powered solutions

Further solutions

FAQs

Frequently asked questions

Exeon’s application security monitoring protects business applications with real-time visibility, advanced threat detection, and privacy-aware security. By analyzing user behavior and processing application-specific logs, it detects anomalies and prevents threats before escalation. With continuous monitoring and advanced analytics, Exeon enhances cybersecurity resilience and ensures operational integrity.

What is OT security?

OT (operational technology) security protects the systems that run physical processes, such as production lines, energy grids, water treatment, hospital infrastructure, and transport networks. Unlike IT, OT environments prioritize availability and safety, often run legacy systems for decades, and can’t easily be patched, scanned, or taken offline.

IT security protects data and business systems, where patching, active scanning, and isolating compromised machines are routine. In OT, those same measures can crash fragile devices or halt production. OT security has to work within these constraints, which usually means passive monitoring and close collaboration between security and operations teams.

Use passive monitoring based on network telemetry you already collect from firewalls, switches, and existing security tools. Nothing is injected into the OT network, so there’s no production impact. From this metadata you can build an asset inventory, map communication flows, and uncover unmanaged devices and remote-access paths.

With a passive, telemetry-based approach, organizations typically see around 90% of communicating assets within about two weeks, depending on the telemetry available. Sensor-heavy projects, by contrast, often take months because of hardware procurement, network changes, and maintenance windows.

Many OT security projects are scoped for near-total coverage from day one. They then stall in procurement, change approvals, and integration before delivering any visibility. Meanwhile, blind spots persist. A visibility-first approach delivers value early and uses what it reveals to guide further investments.

Shadow OT refers to unmanaged or undocumented assets and connections in an OT environment, such as forgotten remote-access paths, contractor laptops, and devices missing from the asset inventory. Passive network monitoring surfaces these quickly, because it shows what is actually communicating rather than what is documented.

Segmentation drift happens when the real network gradually diverges from the intended zone design. Temporary firewall rules that are never removed, overly permissive rules, and new systems connected without updating policy are common causes. Continuous segmentation validation compares observed traffic against intended policy, so drift is caught as it happens instead of at the next annual audit.

These frameworks require organizations to demonstrate monitoring, asset visibility, and incident readiness, not just claim them. You can’t report on assets you haven’t inventoried or prove segmentation between zones you haven’t mapped. Continuous visibility and a behavioral baseline provide time-stamped evidence for audits and make incident reporting deadlines achievable.

No. Exeon complements them. It consolidates OT security alerts, firewall logs, metadata, and infrastructure telemetry into a shared operational view. This helps teams investigate incidents with more context, validate segmentation continuously, and retain historical evidence, so you get more value from the tools you already have.

In OT, containment isn’t purely a security decision. Isolating a system can affect production, safety, and supply chains. Effective response is hybrid: security investigates and advises, operations assesses the operational impact, and both agree in advance on who decides and when to escalate to management and regulators.

Talk to our OT security experts

Talk to our engineering and sales team about Exeon’s immediate, full visibility for critical infrastructure.

Back to Main Menu
Our Products

Why our NDR solution is superior in the market.

AI & Security
Our Swiss-made, AI cybersecurity platform.